
When a cyber incident escalates into a business crisis, many organizations discover too late that their response plans were never designed for real-world pressure. Teams quickly fall back on ad-hoc bridges, spreadsheets, email threads, and disconnected chat logs while decision-making, communications, and coordination become increasingly difficult … just when clarity matters most.
In this one-hour webinar, CGS CyberDefense and Semperis explore how leading security and crisis management practitioners help organizations turn ad-hoc response processes into a more coordinated and resilient crisis management capability.
Using a cyber-crisis-focused lens, the session breaks down what crisis management readiness looks like in practice, from establishing clear roles and escalation paths to improving executive coordination, communications, and operational workflows during high-pressure events.
Attendees will gain practical insights into:
- Common breakdowns that organizations experience during cyber crises
- How structured planning and repeatable workflows improve coordination under pressure
- Why clearly defined and regularly practiced roles and responsibilities are critical before a crisis occurs
- How effective processes for information and data collection improve visibility, coordination, and response execution during an incident
- The role that technology plays in enabling timely decision-making, operational alignment, and crisis management effectiveness
- Why data traceability matters for remediation efforts, legal and regulatory considerations, and continuous process improvement
- Which actions organizations can take to strengthen readiness before the next major incident
Whether your organization is building its crisis management program or looking to mature existing capabilities, this session provides practical guidance for reducing operational chaos, improving cross-functional coordination, and enabling more effective decision-making during cyber events.
Event Details:
Date: Tuesday, October 27 2026
Time: 12:00 PM - 1:00 PM CDT
Register now to secure your spot!
Register Now
Speaker Bio
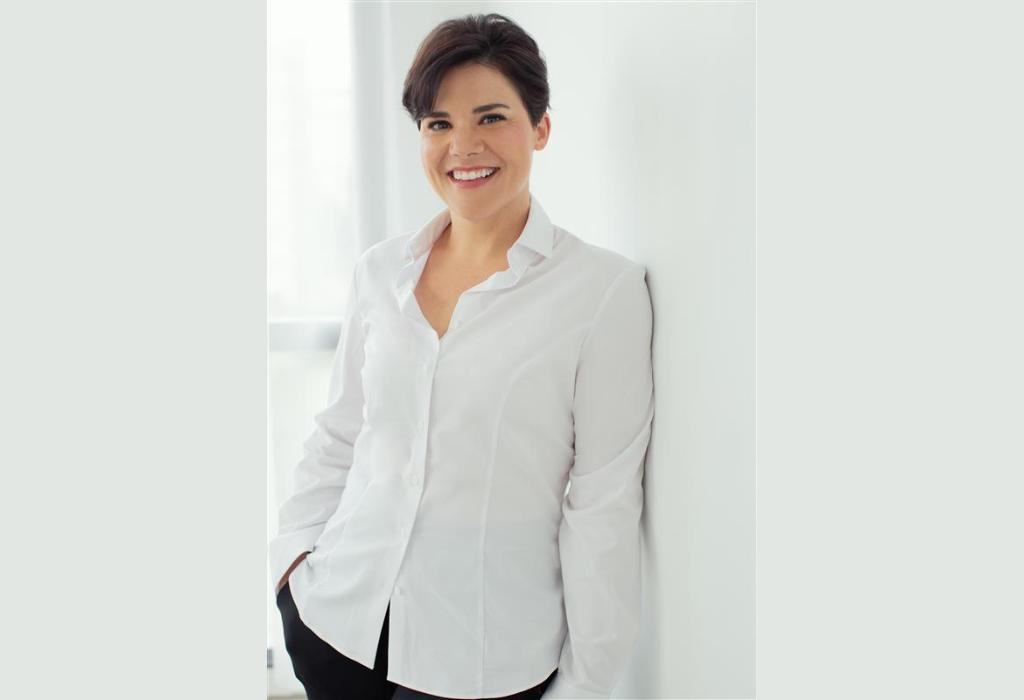
Courtney Guss, Director of Crisis Management
Courtney Guss is Director of Crisis Management at Semperis, with over 20 years of experience spanning cybersecurity, risk management, and crisis response. She specializes in helping organizations navigate high-impact incidents—from ransomware attacks to regulatory reporting—by orchestrating clear, business-aligned response strategies. Courtney is passionate about transforming crisis chaos into operational clarity.
Speaker Bio
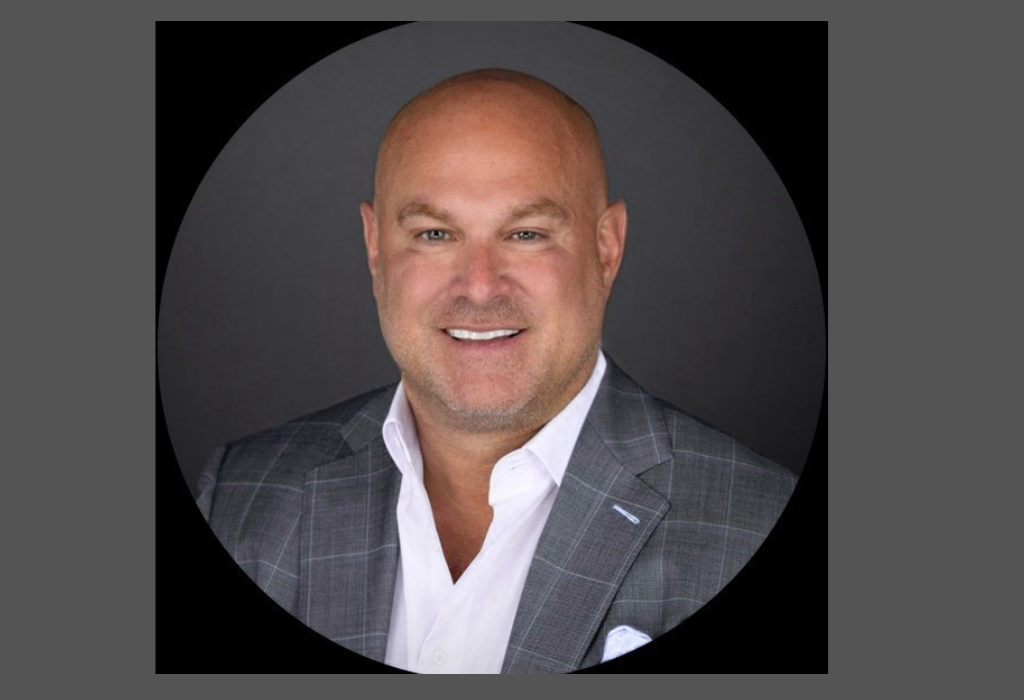
Chris Correia, Chief Executive Officer, CGS CyberDefense
Chris Correia is the Chief Executive Officer of CGS CyberDefense, a trusted cybersecurity advisory and services partner helping organizations navigate the increasing complexity of cyber risk and digital transformation. A seasoned technology and security executive, Chris brings decades of leadership experience across cybersecurity, enterprise technology, and business transformation.
Prior to leading CGS CyberDefense, Chris served in executive security leadership roles, including as a former Chief Information Security Officer (CISO), where he advised executive teams and boards on protecting critical assets, strengthening resilience, and aligning cybersecurity investments with business outcomes. His experience spans building and maturing security programs, managing enterprise risk, enabling innovation, and helping organizations operate confidently in an evolving threat landscape.


© Semperis. All Rights Reserved.
www.semperis.com | privacy@semperis.com